Labels

Pressefreiheit (186) Wirtschaft (168) Österreich (132) IT (128) code (80) Staatsschulden (41) EZB (28) Geopolitik (22) Pensionssystem (17)

2026-09-24

SID (Space Intrusion Detection)


SID (Space Intrusion Detection)

Heinrich Elsigan

September 2026

Download pdf   LaTeX

Introduction

SID is a concept for an intrusion detection system for linux servers in internet or local network including cloud linux servers,

  1. SID daily monitors (and highlights changes to yesterday)

    • all mounted data file systems in detail (except log files, caches, /var/sppol/*)

    • installed kernel, kernel modules lsmod, kernel config and boot (initrd image)

    • current kernel and system settings (/proc file system)

    • attached and registered devices

    • network interfaces and netfilter iptables ip6tables rules

    • all running daemons especially those who allocate listening network tcp/udp socket descriptors

  2. SID hourly monitors

    • available free disk space

    • load average

    • currently active users and daemons

    • all system inter-process communications ipcs lsipc

    • all file descriptors, locks, ... lsfd lslocks,

    • ...

  3. SID permanently monitors

    • successful and failed authentications

    • errors with hints of critical intrusion in all logfiles

    • heavy process or CPU load, which could be an internal privilege escalation or brute force attack

…

Prequel

In UFO TV Series 1970s a SID Space Intrusion Detection, that scans permanently for unidentified flight objects, detects and tracks them and probabilistic calculates most possible ufo’s attack vectors. Ufo series intro & outro
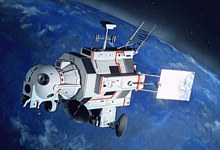
UFO series: SID Space Intrusion Detection

Actions

Regular monitoring activities

SID writes a daily report and highlites all changes to yesterday. filesystem files changed content (sha512), special permissions and all filesystem date time entry changes are emphasized too.

When a concern or intrusion rule matches at daily changes, SID sends additionally an email or SMS. (We don’t want to have too many SPAMs for sysadmin / manager like in Nagios.) Nevertheless SID should send a weekly or montly ’all well and alive’ email message, so that you know, that SID is still operating.

YELLOW and RED alerts intrusion triggers

SID sends immediate an email / sms or Endpoint Service message in case of yellow / red alert at intrusion detection.

… …

SID protection

SID binaries are launched from a readonly not modifyable squash fs mounted image e.g. by snapcraft, a hardware protected usb stick, a LUKS encrypted readonly mounted filesystem or cd / dvd. SID config files should also only mounted rw, when changing them. SID reports could be signed, symmetric or asymmetric encrypted (with passwd or key or X509 certificate).

… …

Epilog

Good luck!

We hope you find SID useful and good luck. To contact me, use the contacts at https://heinrichelsigan.area23.at.

2026-09-02

Better registered® trademarks™ instead of software patents

An addendum to software patents and a discussion with Dr. Paul Rübig on LinkedIn

Software is a composition of many individual components and different algorithms.


Prefer registered® trademark™ over software patents

Nevertheless, it is highly advisable to handle software patents with extreme cautio, as someone else may have already created this or a similar combination of identical algorithms, or someone else may create them without being aware of the patented work.

It is recommended to register complete products or product suites as registered trademarks ™ rather than  via software patents.
Registered trademarks offer better protection against virtually identical copies where only minor layout changes have been made and a code scrambler has been used.

Registered ® trademarks ™ prevent imitation of trademarks, but not of competing products, see

https://www.microsoft.com/en/microsoft-365

https://www.openoffice.org/en/


Authors (in case of humans, companies, NGOs...)
of source code always retain © copyright


Code Snippets

In my opinion, code snippets, such as those used on Stack Overflow, Git, and in various API references, can be copied 1:1 into any source code if they atomic explanations, e.g.:

https://stackoverflow.com/questions/5754879/usage-of-mutex-in-c-sharp


https://learn.microsoft.com/de-de/dotnet/api/system.threading.mutex?view=net-10.0


Basic statements, that are often used identically

switch (pid = fork())

https://man.freebsd.org/cgi/man.cgi?fork(2)

see all Google results for switch (pid = fork())

Last but not least,
limit patent (intelectual property) rights in time

Unlimited IP rights on patents would lead to monopols, which are dangerous for a developing innovative economy.

Pharma drugs have patent and Intelectual property right for some years, later generic pharma products are allowed to enter the market:

https://www.orionpharma.com/newsroom/all-news/articles/science-and-partnering/what-is-a-generic-medicine--and-what-is-good-to-know-about-it/
https://www.fda.gov/drugs/generic-drugs/generic-drugs-questions-answers
https://www.ema.europa.eu/en/glossary-terms/generic-medicine


Term of protection in Austria:
A patent is valid for a maximum of 20 years from the date of application.

2026-09-01

Mathemathische Modellierung

Angenommen es gibt diverse Dinge, die mit einander verknüpft sind und scharfe, unscharfe Zusammenhänge, wie diese auf einander wirken, dann wäre ein Tool nett, dass echt gut mathematisch modellieren kann.

Ich meine ein Tool, dass mehrere plausible mathematische Lösungsmodelle offenbart, sobald man diverse Daten und Formeln eingibt, nach heuristischer Priorität sortiert.

man kann ja wechselseitige Gleichgewichtssysteme durch unterschiedliche Methoden der Mathematik modellieren, wie

  • Polynome n-ten Grades
  • Simplex (lineare Optimierung)
  • Differenzengleichungen
  • Differntialgleichungen
  • Neuronale Netze
  • Gleichgewichtsgleichungen (mit oder ohne resusirven Elemente)
  • Geometrische Modellierung
  • ...
Dabei kann man scharfe oder unscharfe Scopes vorgeben, wie 

Ist wahrscheinlich,
  • dass die Anzahl der zugelassenen Kraftfahrzeuge im Normalfall nicht die Anzahl der Bürger eines Staates übersteigt.
  • dass es zumindest ¼ Geburten pro Jahr gibt im Vergleich zu Todesfällen
  • dass die Strahlkraft der Sonne langsam abnimmt (sehr kleines epsilon)
  • dass Photovoltaikanlagen an Effizienz minimal gewinnen (sehr kleines epsilon)
  • dass die Flussgeschwindigkeit der Flüsse abnimmt
  • dass Turbinen besser optimiert werden können, mehr als die Flußgeschwindigkeit der Flüsse abnimmt
  • dass Computer alle 5 Jahre die doppelte Prozessorleistung bei ¾ der ursprünglichen Eingangsleistung
  • dass man auf jeder neuen Prozessor Hardware nur ein Unix/Linux System innerhalb von 6 Monaten nach Launch hinbekommt....
  • ...
Weiters könnte man exakte Modellierung wählen, oder unscharfe, wo die Daten innerhalb einer gewissen größeres Epsilon Varianz, liegen dürfen.

Zusätzlich können semantiche und pragmastische Regeln eingeben werden, wo das Tool checkt,
Lebewesen => Fortpflanzung 99% Cloning 1% wahrscheinlich
HF Spektrum emitierende Objekte (Radioaktiv, Sterne, Pulsare, ...) => hängt von Masse des Objekts und Emissionsmenge (Halbwertszeit) ab.
Durch semantische Regeln kann das Tool erkennen, ob Datenfehler vorhanden sind, oder kritische ausufernde Datenreihen odeer Formeln als WARNING markieren.

2026-08-25

Personal open cloud VPN box


Personal Cloud VPN is an easy to implement idea

  • to avoid breaking SSL via transparent bluecoat or squid bump
  • to monitor all your input / output traffic
  • to keep 100% control over your input / output traffic

Personal Cloud VPN could be implemented with
...

https://www.f5.com/go/ebook/secure-multicloud-networking-for-dummies


Blue Coat Proxy (now Broadcom Edge SWG / ProxySG) performs SSL/TLS inspection by terminating the encrypted client connection, decrypting and analyzing the traffic, and establishing a new connection to the destination server.


Squid Bump

https://wiki.squid-cache.org/Features/SslBump

https://github.com/satishweb/squid-ssl-proxy

https://support.kaspersky.com/de/kwts/6.1/166244


2026-08-23

Public open Geopolitical Service

US debt clock permanent risk


Opponents of the US, play with the US debt.clock and nay at the right time play that card and that will bring US only in little turbulence, when the FED still works as usual.

https://www.usdebtclock.org/index.html 


Still right tending movement 


There is still a right spin pushment / movement in many societies.
Stake Holders and key players are here the not so often in party or in job successful  older male base and local federal state radio stations and press and internet forums.


Less Fact / Argument  based discussion, more political brawling 


Fact based argument based moderated expert talks disappear from many TV channels.

 Opinion from mostly republican politicians become more weighty and important,

while CEO of big companies or expert seem to have less weight and importance in public discussion / dis-curs. 

Nobody ask either Goldman Sachs or Prof, at university about the opinion next 2-4 years budget,


Argument; The budget from the Democrats will trigger too high debts (if many experts and several calculation proove it) 

Right pushing; Democrats brought so much criminal aliens into US (even if in fact criminality is all time low!) 


China has immense opportunities to get great market segment in European Markets

 During 2026 more and more electronic electrical products became chinese in Austrian local stoes.

The only alternative is expensive Google pixel and some old Motorola. Sony is mostley gone, Samsung reduced the offer.


Risk at democratic party


In case, that republicans will increase right pressure, democrats could make the mistake to not push smart men, like Bruce Schneier, instead looking for most radical pro iranian or most radical socialists, instead of streight and smart people, that really still have a sense of human rights and ethics.

2026-08-18

Mobile Devices → end of Flash, Silverlight, Moonlight, Java Applets, ActiveX

When it comes to browser plugin technologies like Flash, Silverlight, Moonlight or even old Java Applets, I claimed today in the early morn, that those tehcnologies began to die with the raise of mobile devices (most with a unix kernel) and mobile browsers. 


In fact it was the <object>...</object> tag in html, that whose full implementation of all technologies subsequently implied an excessively long and complicated process for mobile device and browser developers.


Died arround 2020 or earlier


https://en.wikipedia.org/wiki/Adobe_Flash

There may exist some flash browser under android, 
but the came too late:
https://play.google.com/store/apps/details?id=com.axio.axiobrowserNew

https://www.ibm.com/docs/en/i/7.5.0?topic=platform-java-applets-applications


https://en.wikipedia.org/wiki/Microsoft_Silverlight


https://en.wikipedia.org/wiki/ActiveX


Html5 + Css with Javascript (TypeScript, Angular) remains


There isn't really an alternative for browser plugin languages we had.  Html5 + Css with Javascript and all derived JS Framrworks like Node.js, TypeScript, Angular cannot map all features of Flash or Java Applets.

2026-08-14

linux encrypting security

This blog article concerns linux encrypting security with public/private key (gpg, RSA, ...) mechanism and X509 certificates hierarchical security.


Levels of linux security  


UEFI Secure boot


Encrypted filesystem 

Linux Unified Key Setup 

Full Disk Encryption on Linux with LUKS


 https://www.linux.com/training-tutorials/how-encrypt-linux-file-system-dm-crypt/ 


filesystem mounting options: fstab

security options: readonly nonexecutable nosuid nosgid 

You can mount /usr as readonly filesystem and remount it rw on updates.

mount -o remount rw  /usr
apt-get update; apt-get distupgrade 
mount -o remount=ro=recursive  /usr

https://unix.stackexchange.com/questions/807127/securing-linux-filesystem-with-mount-options

ro=recursive,noexec=recursive,nosuid  

mount -o remount=noexec=recursive,nosuid  /mnt/{mountpoint}

# /etc/fstab: static file system information.
#
# Use 'blkid' to print the universally unique identifier for a
# device; See fstab(5).
#
# <file system> <mount point>   <type>  <options>  <dump>  <pass>
# / was on /dev/sda4 during installation
UUID=07ceda95-80a7-486c-930b-e9facdf1c073 /        ext4    errors=remount-ro 0       1
# /boot was on /dev/sda2 during installation
UUID=58570ac7-0698-4755-81b7-cc6d59e09f60 /boot    ext4    defaults          0       2
# /boot/efi was on /dev/sda1 during installation
UUID=8B4E-B934  /boot/efi       vfat    umask=0077      0       1
/dev/mapper/sda3_crypt /home           ext4    discard,commit=30,noexec=recursive,nosuid,errors=remount-ro         0       2

snapcraft.io

configure snaps  

using verifiable and updateable readonly snapshots,
instead of installing packages / binaries under /usr

mounting snapshots loopback squashfs (ro,nodev,relatime,errors=continue,threads=single)


Signing containers, kernel images, packages,repositories

https://www.qcecuring.com/blog/code-signing-linux-guide


Signed executables under linux (unix)


https://stackoverflow.com/questions/1732927/signed-executables-under-linux 

Since Solaris 10 & 11 OS perspective all binaries were signed:

https://sourceforge.net/projects/signelf/ 

Linux kernel sign-file.c 

https://github.com/torvalds/linux/scripts/sign-file.c


Signed interpreter scripts under linux


TODO ;(


Verify signed executables at kernel level


TODO ;(

Verify / Validate instruction at hardware level


fetch, add, load, move, jump 

TODO ;(